
DocsPeople and access
Compliance and the audit log
SOC 2 and CIS controls with the findings and evidence for each, and a log of every change made in OpsNexa Online.
Compliance
Compliance lists SOC 2 criteria (CC6.1–CC8.1, A1.2, A1.3) and CIS sections (AWS Foundations, Kubernetes section 5, Docker section 4). Each control shows:
- the open findings that bear on it, from everything OpsNexa Online watches: repositories, live clusters, running images, people and access, leaked keys, drift, least privilege;
- the evidence that a practice is in place: backups, tested restores, access reviews, pull request checks, approvals, fresh scans, the audit log, single sign-on.
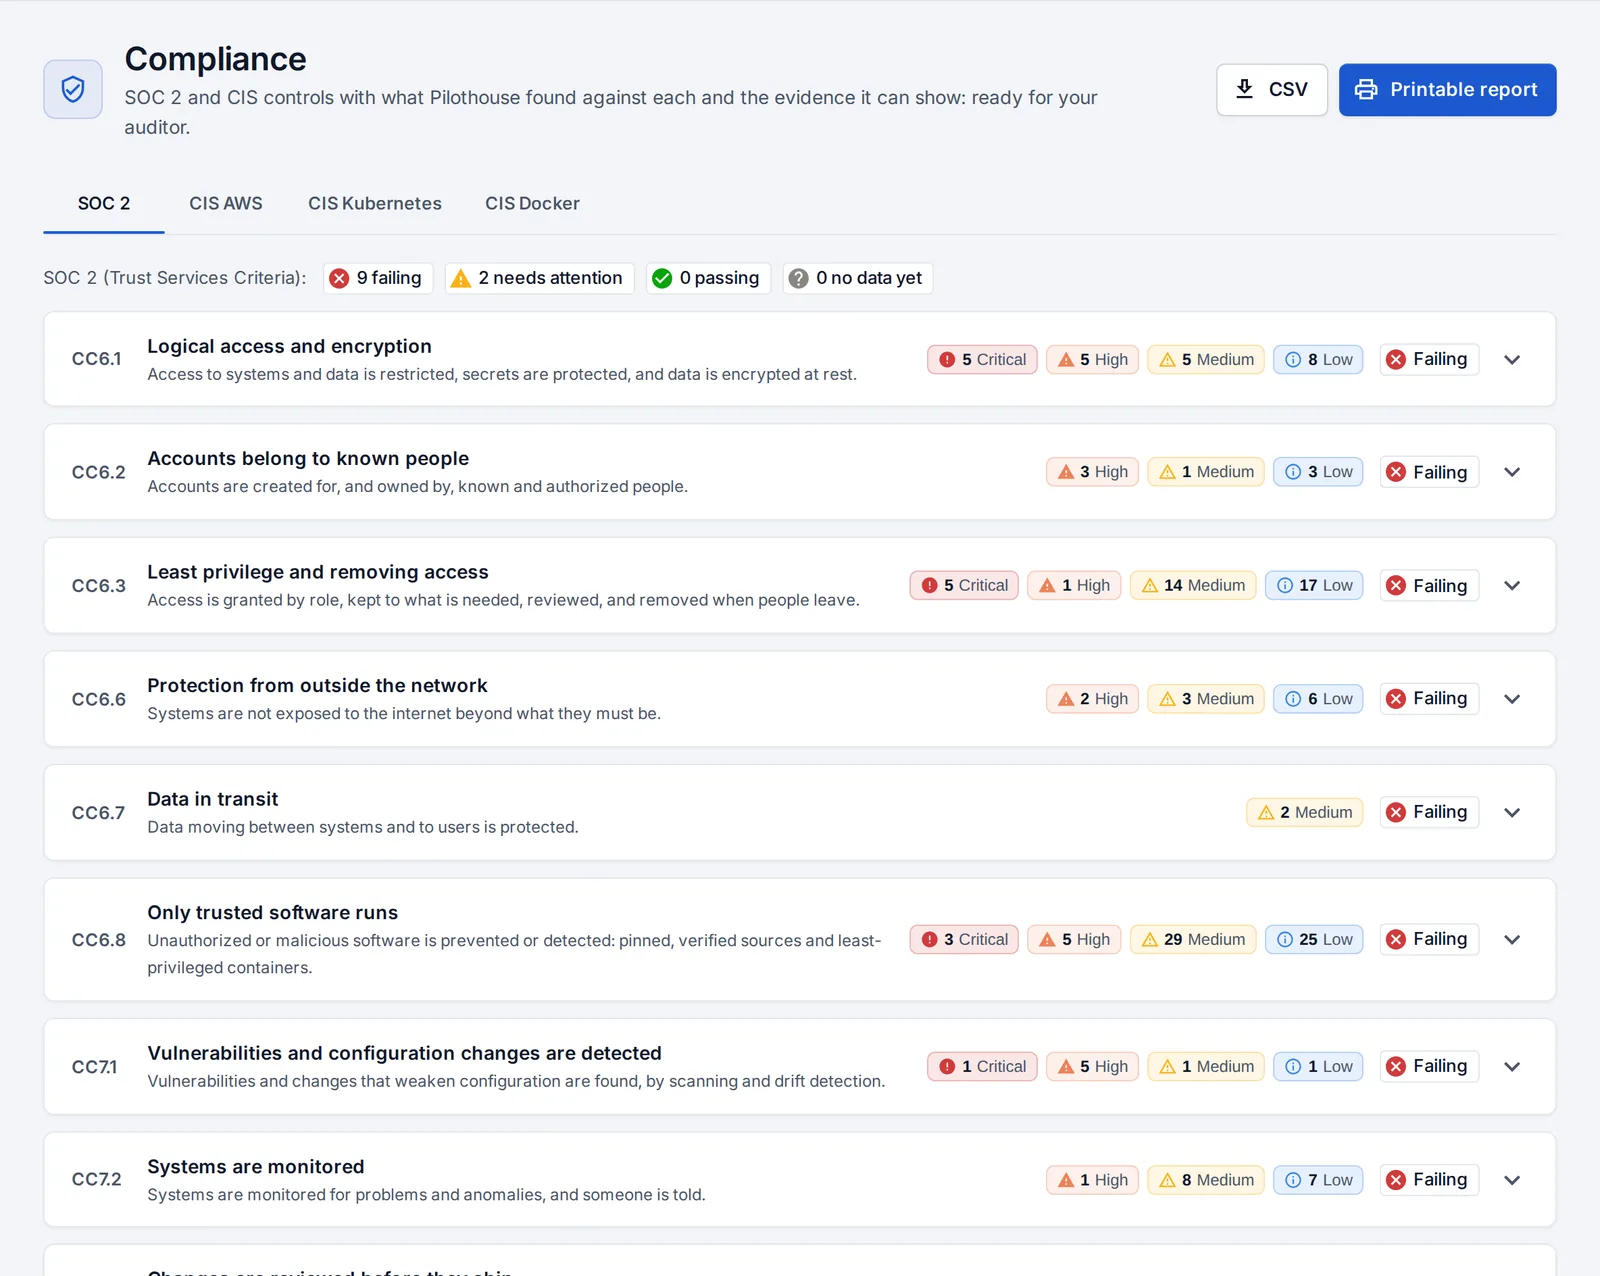
Download a CSV, or a Printable report with a sign-off block.
The audit log
Audit log (admins) lists every change made in OpsNexa Online:
- who made it;
- how: browser, personal or service token, or AI assistant;
- what it was about, and whether it worked;
- from which IP address.
It includes sign-ins, failed sign-ins, and downloads of backups and access exports. Request bodies are never stored.
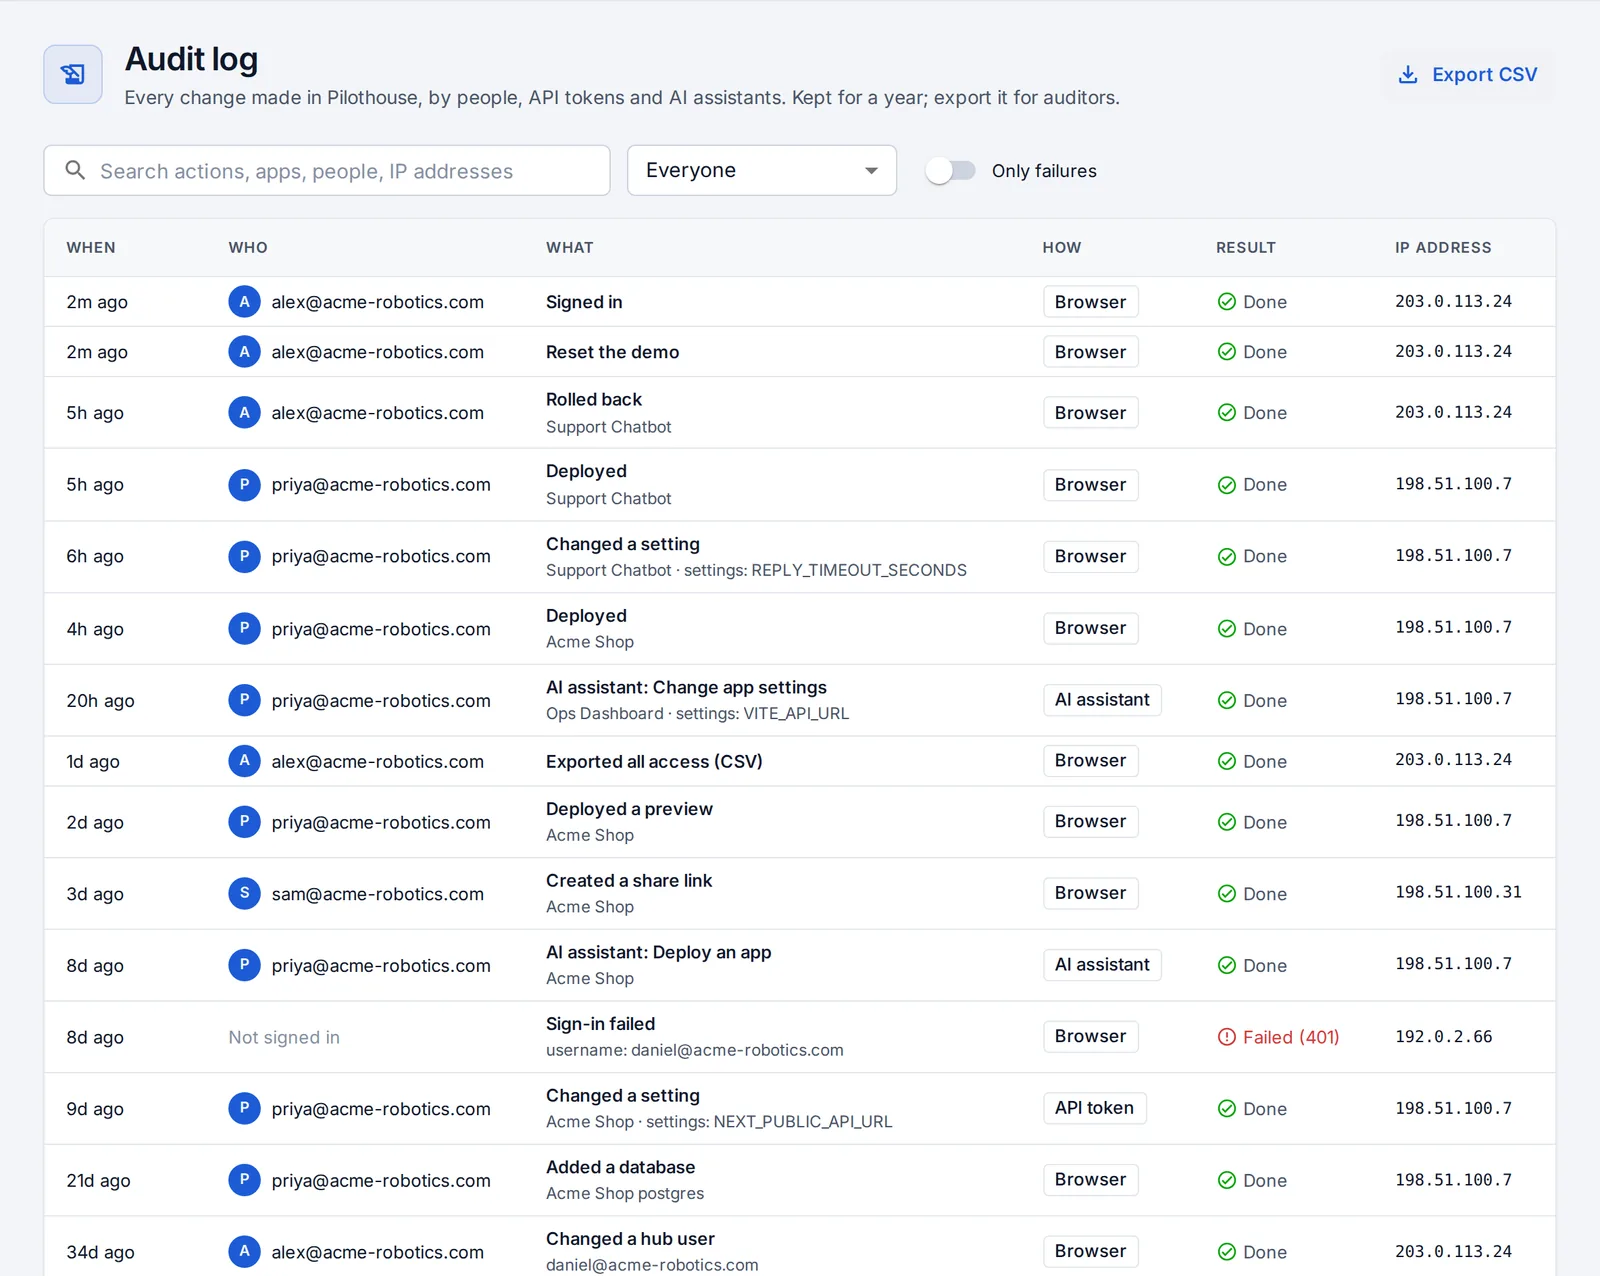
Search, filter, and Export CSV for auditors. Entries are kept for a year.
Something unclear or missing? Tell us, or press the ? at the top of OpsNexa Online for the guide and tours inside the product.